Trading platform & site functionality
PIPHover appears to target a specific pain point: continuing to watch video content with subtitles while you multitask. The landing page messaging suggests a picture‑in‑picture workflow enhanced by subtitle support, a feature many default PiP implementations lack or only partially support. That puts this site squarely in the utility‑software niche rather than anything financial or investment‑related. At face value, the concept is plausible and potentially useful for language learners, remote workers, or anyone who wants to keep tutorials and lectures visible while doing other tasks.
From an infrastructure perspective, domain records indicate the operator uses mainstream providers for DNS and email, and there are signs of integration with Google services commonly seen in lightweight app projects. This can be a positive for availability and security baselines. On the downside, the public‑facing site is sparse: there is no obvious product documentation, changelog, security page, or clear contact pathway. That minimalism is common for side projects but leaves prospective users guessing about platform support, compatibility with major streaming sites, and how actively the tool is maintained. In particular, we did not see a prominent link to a browser store listing or a desktop download, making it difficult to verify distribution channels.
Functionally, a browser extension that injects subtitles into PiP or overlays text across video windows typically requires sensitive permissions. These can include rights to read and modify data on visited sites, capture tab media, interact with video elements, or draw over other content surfaces. Those permissions are not automatically unsafe, but they do expand the blast radius if the tool is compromised, quietly sold, or updated to include undesirable behaviors like tracking or ad injection. Without a clear permissions matrix and a privacy policy spelling out what is stored, where it goes, and for how long, it is hard to judge whether the implementation is conservative or over‑broad.
The landing page does not publish a compatibility matrix for the big platforms (for example Netflix, YouTube, Prime Video, live‑class platforms), nor does it describe known limitations such as DRM contexts that block overlays or break subtitles. Users of similar utilities often report that updates on the streaming platform’s side can suddenly disable features, requiring quick fixes by the developer. When a project is maintained by an identifiable team with active release notes, this is less of a risk; when the operator is opaque and support is unclear, you may be left waiting indefinitely. On usability, a polished tool would normally show guided setup, screenshots, permission prompts explained in plain language, and a path to revoke access or uninstall cleanly. The absence of those elements does not prove wrongdoing, but it does lower confidence in long‑term reliability.
License & regulatory status
Because PIPHover is a non‑financial utility, it is not the sort of service that would be licensed by investment or trading regulators such as the FCA, ASIC, BaFin, or the CFTC. However, that does not put it outside all oversight: if it processes personal data, it is still bound by privacy and consumer‑protection laws that may apply depending on where users reside (for example GDPR in the EU/EEA and UK, or CCPA/CPRA in California). A responsible operator typically publishes a privacy policy, terms of service, and contact details for data requests. The public site does not make these resources readily apparent, which leaves prospective users to assume rather than verify.
We looked for clear claims of compliance, certifications, or third‑party audits on the domain and found none. That absence does not, by itself, indicate misconduct—plenty of small utilities are informal projects—but it does mean you are relying primarily on trust in an unknown developer. We also did not find public regulator warnings or blacklists mentioning piphover.com at the time of review. With small utilities, the risk is less about formal warnings and more about the opacity that prevents users from making an informed decision about data handling.
If PIPHover is distributed through a recognized extension store (such as Chrome Web Store or Microsoft Edge Add‑ons), the listing would usually present the developer name, requested permissions, version history, and user feedback. We did not see a direct link from the site to such a listing. Without that, users cannot leverage the store’s baseline checks, developer identity labeling, and abuse reporting mechanisms. If a listing does exist under a different name or account, the lack of linkage from the official domain makes it harder to validate authenticity and raises the chance that users locate impersonator listings.
User feedback
At the time of this review, we could not locate credible, independent user reviews tied directly to piphover.com on major forums, app stores, or trusted software catalogs. It is possible the tool is new, niche, or distributed privately; it is equally possible that it simply has not yet garnered attention. The challenge for prospective users is that a thin or absent feedback trail makes it hard to distinguish a promising early‑stage utility from a throwaway project that might go unmaintained. For safety‑minded users, the absence of verifiable testimonials or professional reviews is a reason to slow down and validate the distribution channel.
Across the broader category of video overlay and subtitle utilities, we repeatedly see a few recurring complaint themes: surprise permission escalations after installation, unexpected injections of ads or affiliate links on streaming sites, and updates that break functionality with no quick fix from the developer. Another common pain point is data capture without clear benefit—extensions that log browsing behavior or video titles under the guise of “analytics,” without giving users an opt‑out or retention timeline. To be clear, we have not seen such specific allegations directed at PIPHover. We mention these patterns because they are the known risks when permission‑heavy browser utilities are delivered with little public transparency.
If you are curious about PIPHover but cautious, consider controlled testing before committing: install it in a secondary browser profile, limit it to a short list of sites in your extension settings, and monitor whether it requests broader access upon updates. Pay attention to the permissions page in the extension manager and test whether uninstall fully removes injected elements. If a paid tier is offered later, insist on store‑mediated billing and read refund provisions first. These pragmatic steps do not remove risk, but they significantly reduce exposure if the tool does not meet expectations.
Deposits & withdrawals
Because this is not a broker or investment app, typical deposit and withdrawal workflows do not apply. The key financial exposure vector here would be if the operator later introduces a subscription or one‑time purchase. We did not see pricing, a checkout page, or a store‑mediated purchase flow linked from the public site. If you encounter payment requests, treat them as unverified unless they occur through a recognized app store or a reputable payment processor with buyer protections, and make sure terms and refund policies are visible in advance.
If the utility requires creating an account—often via email sign‑in or federated login—you should be able to revoke access and request deletion of personal data. Most reputable operators document those steps and provide a contact or form for data‑erasure requests. In the absence of published instructions, you can still protect yourself: uninstall the extension or application, clear site data for piphover.com in your browser, and if you used a third‑party sign‑in, revoke the app’s access in your account’s security settings. Keep screenshots and timestamps of any requests you send, in case you need to escalate to a data‑protection authority.
If you ever paid for access and feel misled, use the protections available to you. Start by canceling the subscription through the original channel (for example, your app store or payment provider). If the operator does not respond to a refund request, contact your card‑issuing bank to pursue a chargeback, citing non‑delivery, misrepresentation, or unauthorized charges as applicable. Avoid sending additional funds to anyone who contacts you promising a quick refund if you first pay a “verification” or “processing” fee—that is a classic advance‑fee and recovery‑scam pattern.
Why unregulated brokers are risky
The biggest risk with unverified utilities is change over time. Browser extensions update automatically, and a benign early version can later pivot into intrusive tracking, affiliate injection, or worse if the developer sells the project or if their account is compromised. Without a public changelog, code transparency, or a visible security posture, users may not notice the permission creep until after the update lands. This dynamic does not mean PIPHover will do this, but the category risk is real and documented across the ecosystem.
Opacity also complicates remedies when things go wrong. If an extension ships an update that suddenly requests access to read and change all your data on every site, you want to know who is responsible, how to roll back, and where to file a formal complaint. When the operator’s identity, jurisdiction, or contact pathway is unclear, you lose leverage and time during that evaluation. Clear terms of service and privacy notices can mitigate this by explicitly stating data uses, retention, and dispute avenues—but those materials are not readily visible on the site.
Finally, unregulated does not mean unaccountable. If personal data is processed, regional privacy frameworks can apply, and consumer‑protection regulators can act on deceptive practices. That said, enforcement is typically slower than the lifecycle of a small utility, which is why user diligence is your first line of defense. Prefer vendors with a track record, open or at least well‑documented code paths, and store listings that show developer identity and reviews you can independently verify.
How to get help if you’ve been scammed
If you have already paid money connected to piphover.com and suspect misrepresentation, act quickly. Contact your card issuer or bank to initiate a chargeback and freeze or replace any compromised cards. Document everything: receipts, emails, screenshots of the website or extension prompts, and any error messages. Do not send additional funds to anyone promising expedited refunds or unblocking access—advance‑fee and recovery scams often target victims at this stage.
Report what happened to authorities aligned with your location. In the United States, file a complaint with the FTC and the FBI’s Internet Crime Complaint Center at IC3; in the United Kingdom, report via Action Fraud. If your issue relates to a browser extension listing, use the abuse reporting tools in the Chrome Web Store or other relevant platform. For privacy concerns, consider submitting a complaint to your national data‑protection authority, especially if deletion or access requests go unanswered. These reports build an official trail and improve your chances if you seek redress.
For guided assistance, contact our team at reportscammedfunds.pro. We review documentation, help you structure chargeback narratives, and advise on escalation avenues that fit your jurisdiction and payment method. Include timelines, transaction IDs, communication threads, and any developer responses—well‑organized evidence increases the probability of a positive outcome. Even if the loss is small, early intervention can prevent further damage and help warn others.
Conclusion
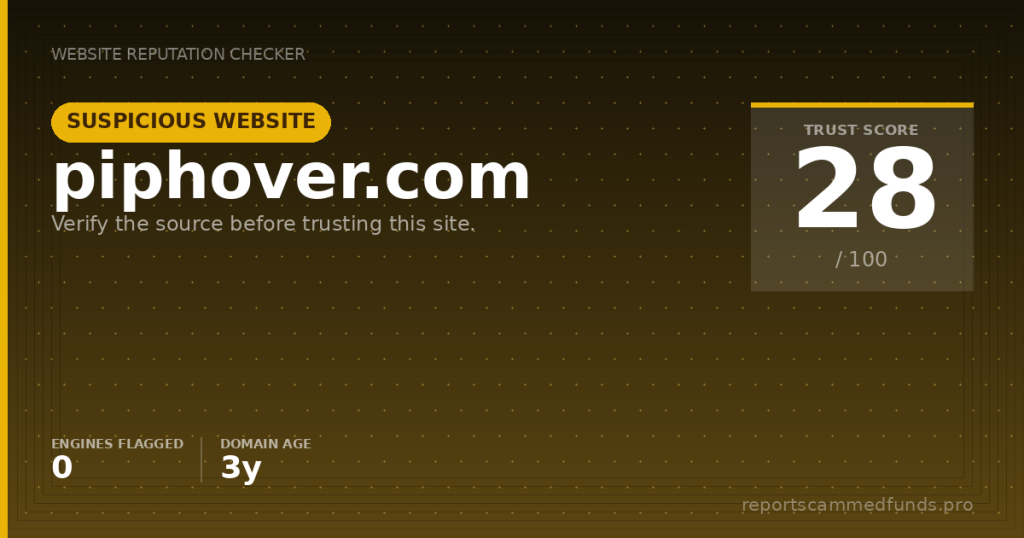
PIPHover pitches a practical idea—keep watching what you love with subtitles while multitasking—but reveals very little about who is behind it, how the product is maintained, or how data is handled. Our automated checks did not flag overt security issues, and the domain sits on broadly reputable infrastructure. Yet the operator’s opacity, sparse site content, and absence of a verifiable distribution channel mean users are being asked to trust what they cannot verify. In this context, caution is not paranoia; it is basic hygiene.
If you decide to try the tool, insist on guardrails. Prefer installing from a recognized store listing that you can trace back to the official domain, and read the requested permissions carefully. Test in a secondary browser profile, restrict site access where possible, and uninstall promptly if permission creep or odd behavior appears. If payments are requested, use only platforms with buyer protections and make sure you can cancel easily.
Our bottom line: not an outright scam based on what we can see today, but not a site we would recommend adopting widely without further transparency. The developer can enhance trust quickly by posting a privacy policy, terms, support contacts, and a direct link to a signed, store‑hosted distribution listing with a visible developer identity. Until then, treat piphover.com as a cautiously interesting utility with unresolved due‑diligence gaps.