Trading platform & site functionality
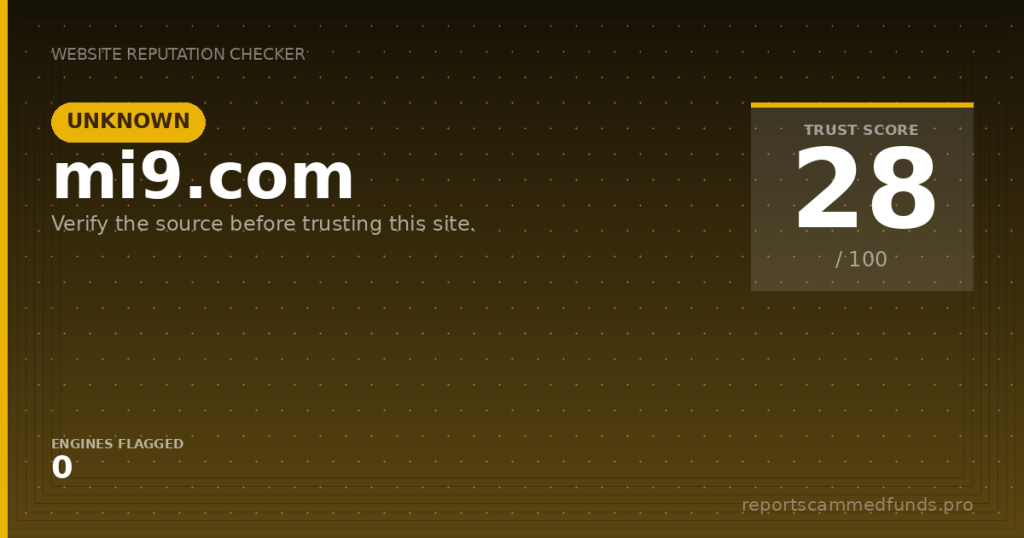
At the time of our assessment, mi9.com did not load a functional homepage or any interior pages that we could verify. Without visible content, there is no on‑page explanation of services, pricing, support options, or ownership. This absence is not proof of wrongdoing, but it creates a vacuum of information that prevents users from making a confident decision about engaging. When a site carries a short, brandable domain yet provides no context, the burden shifts to the operator to prove who they are and why a visitor should trust them.
The name Mi9 has been associated historically with different, unrelated entities, including a media business in Australia and a retail software provider that use other domains for their official presence. Because of that, a domain like mi9.com can easily be conflated with better‑known brands—an environment ripe for misdirected emails, mistaken invoices, or even opportunistic impersonation. We could not confirm whether this domain is connected to any known company or if it is a legacy asset with no current corporate use. That ambiguity alone is a reason to proceed with heightened caution.
From a user‑experience standpoint, a trustworthy corporate site typically discloses the basics: an About page that names the entity, a physical address, an executive or team listing, and a contact page with verifiable channels. It will also publish a privacy policy and terms of service, often with date stamps and governing‑law references. None of those baseline elements were observable on mi9.com during this review. Without them, any potential visitor or prospective client has no reliable way to understand obligations, liabilities, or recourse.
If this domain is intended as a corporate landing page, its current state does not meet industry norms for transparency or functionality. Even a minimal placeholder site would normally declare forthcoming services, provide a single support email, or reference a parent company. The complete lack of accessible content means the best course for a user is to independently verify claims through external sources and direct corporate channels. Until the operator publishes durable disclosures, the safest assumption is that the site is not ready for transactional or data‑sensitive interactions.
License & regulatory status
There is no evidence that mi9.com is offering brokerage, investment, or retail‑trading services, so financial regulation may be inapplicable. However, should the site or any party using the mi9.com domain solicit investments, trading accounts, or deposit‑taking activities, formal authorization would be required in most jurisdictions. Prospective users should verify any such claims against official registers: the UK’s FCA Register, Germany’s BaFin database, Italy’s CONSOB records, Australia’s ASIC professional registers, Switzerland’s FINMA, and the US NFA/CFTC registries for derivatives.
We did not encounter any license numbers, disclosures, or legally required statements on mi9.com. In general, brokers and investment advisors must display precise license identifiers, sometimes with regional branch references and complaint channels. If you ever see regulators’ logos, seals, or vague claims like ‘fully compliant with ESMA rules’ without a verifiable certificate or registry link, treat it as a red flag. A legitimate firm’s credentials can be independently verified on the regulator’s official site—not by screenshots hosted on the company’s own pages.
False‑affiliation claims are a classic tactic across scam categories: an operator asserts ties to a well‑known entity or regulator, counting on users not to verify. The brand name Mi9, because of its prior use by unrelated companies under different domains, is a potential magnet for such claims. If you receive outreach from an address at mi9.com claiming to represent a known brand, cross‑check the domain used by the genuine company and call their published corporate phone number to confirm. Never rely solely on email signatures or presentation decks.
For non‑financial B2B services—software, marketing, consulting—regulatory licensing may not be required, but corporate identity still matters. A legitimate outfit typically provides a company registration number, VAT or tax identifiers where applicable, and a real street address that can be validated. If those details are not forthcoming, or if the entity encourages payments to personal accounts or requests cryptocurrency for ‘setup fees’, proceed as though you are dealing with an unverified operator. The absence of clear legal grounding materially increases counterparty risk.
User feedback
Our review did not surface a body of consistent, first‑hand customer feedback specific to mi9.com. Search results around the name ‘Mi9’ tend to reference unrelated brands that operate on other domains, which complicates any attempt to attribute experiences to this particular site. The lack of reviews does not confirm safety; it simply means there is no usable peer history to weigh. In opaque situations like this, the absence of a review trail should be treated as an additional reason to slow down and verify.
Where confusion with a brand name exists, a common scenario is misdirected communication: a vendor or client mistakes one domain for another and shares sensitive documents or invoices to the wrong place. While we did not collect verified reports of that happening with mi9.com, the risk is structurally present given the generic brand and lack of operator transparency. Any inbound email from a domain that lacks a public footprint deserves extra diligence. Check whether the sender’s domain matches the official website of the company they claim to represent.
There were no credible, dated, and detailed complaints we could tie indisputably to mi9.com, such as withdrawal blockages, surprise KYC after deposit, or managed‑account losses—issues that are typical of unregulated trading sites. However, the absence of such markers should not be read as a positive; it may simply reflect a dormant or little‑used domain. Equally, a dormant domain can be reactivated quickly for a campaign, including phishing or invoice fraud, if controls are weak. That lack of a track record makes proactive verification essential.
If you have interacted with parties using the mi9.com domain, consider sharing your experience with consumer‑protection forums or relevant authorities. Detailed reports—dates, sums, communication logs—help other users and investigators differentiate accidental confusion from deliberate deception. Keep in mind that ambiguous one‑line posts are of limited value; fact‑rich accounts enable better collective risk assessment. Until such evidence builds, the prudent stance is to assume nothing is verified and to demand documentary proof of claims.
Deposits & withdrawals
Because mi9.com does not present itself as a financial platform, this section focuses on payment and data‑handover risks common to unverified corporate sites. If anyone using this domain requests prepayment for services, insist on a formal quote, an executed contract that identifies a legal entity, and a proper invoice. Payments should go to a corporate account in the same legal name that appears on the contract, not to personal accounts or cryptocurrency wallets. Requests for ‘expedited onboarding fees’ or ‘one‑time setup deposits’ without documentation are a classic advance‑fee pattern.
If you are presented with bank details, verify them independently, not by replying to the same email thread. Call the company using a phone number you source yourself—ideally from a regulator’s registry or a longstanding corporate website—and confirm the beneficiary name and IBAN. For cross‑border wires, match the jurisdiction to the company’s claimed headquarters; inconsistencies can indicate a mule account. Card payments offer some chargeback recourse, but do not assume recoverability if the payee is obscure or the transaction is coded as a ‘high‑risk’ merchant category.
Some operators try to steer customers into cryptocurrency or gift‑card payments, citing speed or discounts. Treat those requests as near‑certain red flags because such transfers are difficult to reverse and are favored by fraudsters. If you are offered a discount in exchange for paying in crypto or asked to split a payment across multiple wallets, stop and reassess. Legitimate B2B sellers rarely, if ever, rely on that model, and reputable advertising or software vendors can accommodate standard invoicing and card‑based settlement.
If you already shared personal data through a form or email tied to mi9.com, consider sending a data‑erasure request under GDPR/CCPA where applicable and monitor your accounts for unusual activity. Keep records of every interaction—emails, attachments, screenshots, timestamps—as they can be vital if you seek a refund or file a complaint. Should the party fail to honor deletion or data‑access requests, escalate through your data‑protection authority. Data control and documented processes are markers of a serious operator; silence or evasiveness is a warning sign.
Why unregulated brokers are risky
Engaging with an unverified site carries structural risks that extend beyond money. Without a named legal entity and governing terms, users lack clarity on jurisdiction, dispute resolution, and data handling. In the event of a disagreement or a suspected fraud, it can be practically impossible to assert rights if the counterparty’s identity is unknown. This is why transparency and traceability—addresses, registration numbers, named executives—are not formalities but core safety features.
Even when a site does not solicit investments, it can still be used as a vehicle for social engineering. Dormant or low‑visibility domains are sometimes reactivated for phishing campaigns or invoice‑spoofing schemes, exploiting the appearance of legitimacy that a clean .com domain confers. An email that references a seemingly professional domain can be enough to nudge a harried team into paying an invoice or sharing credentials. The operating model of many scams is to borrow reputation from names that appear familiar or neutral.
There is also the risk of operational instability. A site without durable content may be here today and gone tomorrow—sometimes by design. If that site held your documents or payment details, you might have no way to know how they were stored or who else accessed them. Conversely, if the domain is parked, you might later see an entirely different operator take control, leading to further confusion about whom you previously engaged with.
Given these risks, the standard for comfort should be higher when a website is opaque. Before sending sensitive files, paying retainers, or onboarding to tools promoted via a bare domain, insist on cross‑channel confirmation. Validate the entity on business registries, ask for references, and verify domain ownership alignment with the claimed company. Caution is not cynicism—it is a rational response to information gaps that materially affect your ability to seek recourse.
How to get help if you’ve been scammed
If you sent money in connection with mi9.com and now suspect a problem, act quickly. Contact your bank or card issuer to request a chargeback or wire recall, explaining that you may have paid an unverified or misrepresented counterparty. If cryptocurrency was used, notify the exchange or wallet provider immediately and open a compliance ticket with all transaction hashes and communications. Preserve all evidence: emails with headers, invoices, chat logs, and any files you were sent.
File formal reports with the appropriate authorities in your jurisdiction. In the United States, submit a complaint to the FBI’s Internet Crime Complaint Center (IC3). In the United Kingdom, report via Action Fraud. In the European Union and elsewhere, consult your national cybercrime or consumer‑protection agency, and consider logging a cross‑border complaint through econsumer.gov. These filings help establish patterns that can lead to takedowns or enforcement even when individual sums are modest.
For tailored case guidance and documentation support, you can reach our team at reportscammedfunds.pro. We assist victims in structuring evidence, coordinating with banks and exchanges, and avoiding secondary ‘recovery scam’ operators who promise fast refunds for an upfront fee. Use a secure device, compile a timeline of events, and include screenshots of the website or emails you interacted with. We will not ask for remote access or for you to install software—red flags you should reject from anyone.
If you only shared data but did not pay, you should still take precautions. Change any passwords you revealed or reused, enable multi‑factor authentication, and consider a fraud alert with your credit bureau if sensitive identity information was exposed. Send a written request to the operator for data deletion and a copy of any information they hold about you, and set a calendar reminder to follow up. Whether or not you pursue funds recovery, documenting your steps now will strengthen any future claims.
Conclusion
Mi9.com, as it appears today, is an opaque domain with no accessible content and no clear operator disclosures. We did not find definitive evidence that the domain is being used for fraud, but we equally found no evidence that would justify trust or payments. The name itself invites confusion with unrelated brands that operate on other domains, creating an environment where misdirected communication or impersonation attempts could thrive. In risk terms, this is a classic information‑asymmetry case, and the asymmetry is not in your favor.
Our recommendation is simple: do not share sensitive data or send funds to parties using the mi9.com domain until you have independently verified their identity through off‑channel means. Demand corporate documentation, verify bank beneficiaries, and confirm domain alignment with any well‑known brand that the party claims to represent. If you cannot obtain those assurances, walk away; the cost of a missed opportunity is almost always lower than the cost of a bad interaction.
If you are a business that has received an invoice or an employment applicant communication from mi9.com, implement a call‑back verification procedure using numbers sourced from official channels. Train your team to recognize advance‑fee patterns, pressure tactics, and requests to switch to crypto or gift‑card payments. Establish a single internal point for vendor onboarding to reduce the chance of a hurried approval based on a familiar‑seeming domain name.
Should the operator of mi9.com later publish transparent corporate details—company name, registration number, physical address, verifiable contact channels—and provide consistent content over time, we will update our view accordingly. Until then, the lack of accountability and the elevated risk of brand confusion justify a cautious stance. Treat the domain as unverified, and proceed only under strict due‑diligence protocols.