Trading platform & site functionality
At first glance, keepandroidopen.org operates as a single-purpose campaign microsite, focused on a specific warning about proposed Android policies in 2027. The content resembles an advocacy statement more than a commercial offer, with a headline asserting a significant change to app availability absent developer registration. Such sites typically exist to influence opinion or galvanize a developer or user community rather than to transact. Notably, we did not observe an e-commerce checkout, investment pitch, or an account login. That simplicity, while normal for an advocacy page, also limits transparency because there are few sections where one might learn about the operator’s background or governance.
From a technical perspective, the domain resolves through a mainstream content delivery network and uses A records commonly associated with static hosting, which is consistent with a lightweight, brochure-style site. This tends to make browsing fast and reliable, but it also makes it inexpensive for virtually anyone to publish a polished page quickly. We did not encounter pop-up prompts to deposit funds, download executables, or connect a crypto wallet during our checks. The site’s language is concise, with a tagline framing the risk as imminent and sweeping, which is a common persuasive pattern in advocacy. When a site leads with urgency, we look for substantiating links or primary-source documents; here, those were not immediately evident.
Navigation appears minimal, which is typical for short-lived campaigns or time-limited calls to action. If there are forms present—such as a contact form, newsletter sign-up, or petition-style entry—users should note what information is requested and whether a privacy policy or data retention statement accompanies the fields. We did not see a page structure that made legal or contact details obvious from the landing view, which means additional clicks or an off-site search may be needed to find them, if they exist. The absence of heavyweight scripts and dynamic dashboards suggests no complex account system is running in the background. That lowers the risk of transactional abuse but raises the importance of verifying who is behind the message before you volunteer personal data.
On balance, the functionality aligns with a standard static campaign: a single message, a narrow set of actions, and minimal infrastructure. That in itself is not suspicious, but it leaves the burden of verification on the reader, especially when bold claims are presented without clearly cited sources. Because the infrastructure is easy to spin up, the same design can host legitimate speech or opportunistic misinformation with equal ease. If the site invites you to follow social channels or share content, do so with the same caution you would apply to any unverified campaign—avoid connecting it to sensitive accounts or granting broad permissions through third-party login prompts. Treat the site as a starting point for research, not as an authoritative endpoint.
License & regulatory status
A site advocating for platform policy is not expected to hold a financial license, and we did not see any claims of regulation by financial authorities such as the FCA, BaFin, ASIC, CONSOB, CFTC, or ESMA. That is appropriate for an informational campaign. However, if the operator collects personal data through forms, it still owes users basic disclosures under consumer protection and privacy laws applicable in many jurisdictions, such as GDPR in the EU or CCPA in California. We did not see prominent, clearly labeled legal pages at first pass, which suggests users should look carefully for a privacy policy and terms of use before submitting information.
We also looked for false affiliations or logos implying endorsement by regulators, government bodies, or major nonprofits. No such regulator seals or license numbers were surfaced in our on-page review. Absence of false claims is a positive sign, but it does not shed light on who actually runs the site. If the page references industry groups, foundations, or coalitions, those claims should be cross-checked on the named organizations’ own sites to confirm the relationship. A genuine coalition partner will generally list the campaign back on their official domain.
We found no regulator warnings about this domain in the public sources we track at the time of writing. That said, young campaign sites often fly under the radar and may not have been assessed by authorities or watchdogs yet. If the site begins soliciting donations or selling memberships, regulatory expectations change: payment processing obligations, charitable solicitation registrations in some regions, and clearer disclosures become relevant. Until then, treat this as unregulated informational content and validate its assertions using primary sources, such as Android developer documentation or official announcements from Google, rather than relying solely on the site’s framing.
User feedback
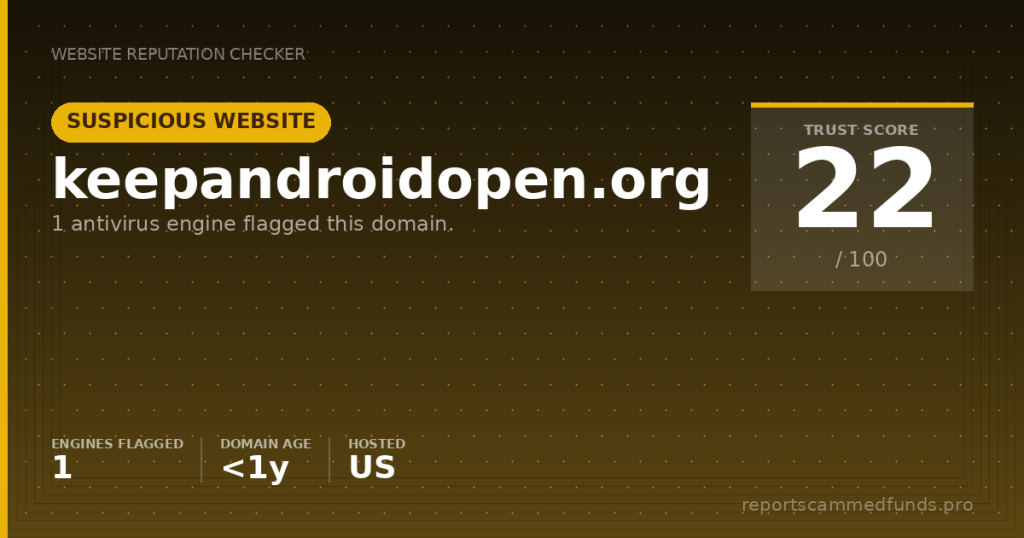
Public feedback on keepandroidopen.org appears limited, which is common for a domain that is less than a year old. We did not locate a broad base of independent reviews, long-form analyses, or mainstream press coverage that would lend external credibility. That does not automatically discredit the site’s message, but it means the signal-to-noise ratio is thin and easy to manipulate through coordinated social posting. In these situations, the most reliable approach is to weigh the site’s claims against neutral documentation and to consider the diversity and reputation of voices promoting or criticizing it.
We did not find recurring complaints indicating classic scam behaviors such as withdrawal blockages after payment, surprise KYC after deposit, or managed-account losses—patterns that are typical for investment fraud but inapplicable here because the site does not appear to take money or hold user balances. Likewise, we did not encounter claims of malware distribution tied to downloads from this domain. However, one security engine did flag the URL, which might be a generic or reputation-based classification rather than a direct detection. False positives are not rare for newly minted, static campaign sites hosted behind large CDNs.
If there are social accounts associated with the campaign, scrutinize them for authenticity markers beyond a verified badge: posting history, cross-references from known organizations, and consistency of messaging across platforms. Be skeptical of comment sections filled with generic praise, copy-paste talking points, or accounts created recently with little activity—signs of astroturfing that can inflate perceived support. Absence of critical discussion can also be a red flag in policy debates; legitimate movements typically attract reasoned pushback. Given the current lack of independent, high-quality feedback, we recommend treating the site as a claim that still needs external corroboration.
Deposits & withdrawals
Because keepandroidopen.org does not present itself as a financial service, there are no clear deposit, withdrawal, or account balance functions to evaluate. We did not see prompts to connect payment cards, bank accounts, or crypto wallets in our review window. If the site ever adds a donation button, verify that the payment processor is a known, reputable gateway and that the recipient entity is clearly named with a traceable legal presence. Legitimate campaigns usually route payments through established platforms and provide receipts that include the operating organization’s name.
In the absence of money flows, the primary risk shifts to data handling. If a form asks for your email, phone, or demographic information, consider what you receive in return—an update, a downloadable resource, or a petition confirmation—and whether the privacy policy states how that data will be used, shared, or retained. Avoid supplying sensitive information like government IDs, full addresses, or payment details unless a clear and legitimate need is demonstrated and backed by policy disclosures you can review. Be wary of any sudden change from advocacy messaging to urgent donation demands, especially if they involve irreversible methods like crypto transfers.
Should you have already made a contribution through a link associated with the site and now regret it, act quickly. For card payments, contact your bank or card issuer and ask about a chargeback, providing dates, amounts, and any communications you received. For platform payments (for example, a digital wallet or payment processor), open a dispute through their resolution center and document how the solicitation differed from what was promised. If you sent funds by wire or crypto, traditional recovery is harder, but timing and documentation still matter—preserve messages, receipts, and transaction IDs so investigators have a trail to follow.
Why unregulated brokers are risky
Unregulated advocacy sites carry a different kind of risk than unlicensed brokers, but the core principle is similar: you have limited recourse if the information is misleading or your data is mishandled. There is no investor-compensation scheme, ombudsman route, or regulator to appeal to if your email is sold or your consent is stretched into unrelated marketing. Policy-campaign pages often emphasize urgency to secure quick sign-ups, and in that rush, disclaimers and data rights can be minimized or omitted entirely. Without a named operator, accountability is effectively an honor system.
Another risk is narrative capture. A site can present a technically true but incomplete picture to steer readers, especially in complex subjects like app distribution policies, developer compliance, and platform security. Without references to primary materials—official policies, developer program terms, and regulator statements—it is hard to test the framing for bias. That does not make the campaign illegitimate, but it reinforces the need to consult original documents and a range of reputable analyses before adopting the site’s conclusions. A healthy skepticism helps counter both genuine mistakes and deliberate spin.
Finally, some bad actors co-opt genuine-sounding causes to build contact lists that are later monetized or repurposed. The step from an advocacy landing page to unsolicited fundraising, affiliate offers, or even unrelated political messaging can be short and opaque. If you start receiving messages that go beyond the site’s stated topic, opt out, and consider reporting the misuse. Treat petitions and newsletter sign-ups as data transactions: you are giving something of value, and you should only proceed if you are comfortable with how it may be used.
How to get help if you’ve been scammed
If you engaged with keepandroidopen.org and now believe you were misled or your data was mishandled, there are concrete steps you can take. Start by securing your accounts: change passwords associated with any email you provided and enable multi-factor authentication. If you made a payment, contact your bank or card issuer immediately to request a chargeback and place a note on your account for suspected deceptive solicitation. For platform payments, open a dispute with the payment provider and describe precisely how the appeal differed from the promised purpose or disclosures.
Report the incident to the appropriate authority in your jurisdiction. In the United States, file a complaint with the FTC and the Internet Crime Complaint Center (IC3); in the United Kingdom, report to Action Fraud; in the European Union, contact your national consumer authority or local police; in Australia, use ReportCyber and consider notifying ACCC Scamwatch; in Canada, contact the Canadian Anti-Fraud Centre. Include the domain name, dates, amounts, communications, and any screenshots you have. The sooner you report, the better the chance of preventing further harm to others and documenting patterns if multiple complaints arise.
You can also request guidance from our team at reportscammedfunds.pro. We handle case assessments for online fraud and deceptive practices and can help you triage next steps, organize evidence, and coordinate outreach to banks and platforms. Visit reportscammedfunds.pro to describe your situation, and our staff will advise whether chargebacks, platform disputes, or formal regulatory reports are your best path. Even if your loss involves data rather than money, early action to contain exposure—password resets, account monitoring, and opt-outs—can meaningfully reduce downstream risk.
Conclusion
Our assessment of keepandroidopen.org is cautiously skeptical. The site looks like a minimal advocacy page hosted on mainstream infrastructure with a valid certificate and no obvious payment captures, which points away from an outright scam. Yet the combination of a very young, privacy-shielded domain, a lack of named ownership, and a single reputation engine flag compels prudence. Until the operator is identified and the claims are supported with primary sources, the safest posture is to read but verify elsewhere.
If you are sympathetic to the cause, your safest engagement is low-risk sharing or independent research rather than form submissions or donations. Seek corroboration from recognized developer organizations, established digital rights groups, and official Android developer documentation. If the site links to social profiles, confirm that those accounts are acknowledged by credible organizations, not just self-asserted. Remember that effective advocacy welcomes scrutiny and provides footnotes, names, and contacts; opacity is a choice.
We do not currently label this domain as malicious or a phishing host, but we do not consider it fully trustworthy either. Treat it as a claim in need of evidence, not as an authoritative source. Keep your guard up, keep your wallet closed unless a reputable processor and named organization are involved, and keep your identity safe by limiting what you share. If anything about your interaction goes wrong, document everything and seek help through your bank, relevant authorities, and reportscammedfunds.pro.