Trading platform & site functionality
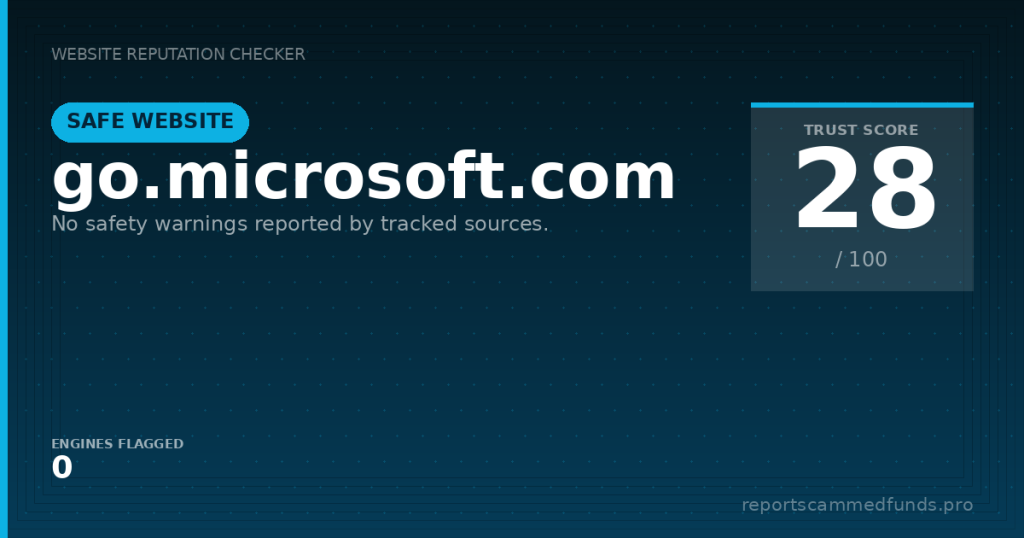
The domain go.microsoft.com functions as a Microsoft-controlled redirector, commonly used to route users to documentation, support articles, downloads, and product pages. In many cases, links are parameterized with identifiers that map to a specific destination within Microsoft’s ecosystem, such as learn.microsoft.com, support.microsoft.com, or other official properties. This type of redirect tooling allows Microsoft to maintain stable, short, and localized links even as underlying content moves over time. Users will typically see their browser traverse directly to a Microsoft-branded page with a valid certificate and familiar design elements.
Because go.microsoft.com is a redirector rather than a content site, it usually displays no standalone pages or marketing language of its own. Instead, the experience is one of near-instant handoff: clicking a go.microsoft.com link transitions you to the target resource, often with region or language awareness based on your settings or location. The design is convenient, but it also means you can’t preview the final destination just by looking at the link text. Ideally, the redirect should point only to official Microsoft domains, and that is how the service is intended to operate.
In practice, the redirector supports product teams and documentation authors by keeping links consistent across software prompts, knowledge base articles, and update notices. Over time, some older links may lead to retired or reorganized content, leading to a 404 or a generic landing page that advises where the material has moved. These outcomes are more consistent with link rot than malice and can be mitigated by finding the updated resource via Microsoft’s site search or verified navigation from the home pages. From a usability standpoint, the behavior is normal for a large publisher evolving its documentation stack.
License & regulatory status
As a non-financial domain under microsoft.com, go.microsoft.com is not expected to hold licenses from financial regulators like the FCA, BaFin, ASIC, or the CFTC. Instead, the relevant trust lens here is corporate ownership, brand control, and adherence to web security standards. Microsoft is a publicly traded U.S. corporation subject to securities law reporting, data protection frameworks, and consumer protection obligations across jurisdictions where it operates. No credible regulatory body is known to have issued warnings against this specific redirector domain.
On the technical trust side, the parent domain uses industry-standard TLS with certificates issued to Microsoft’s corporate identity, and the browser padlock should reflect a valid certificate chain. The microsoft.com ecosystem typically enforces modern security headers, including HSTS on parent domains, to reduce the risk of downgrade or interception attacks. While such controls do not eliminate user-facing risks like phishing, they do indicate professional security hygiene commensurate with a large technology vendor. Users should still observe the destination domain after redirection and confirm it remains within Microsoft’s web properties.
Some community discussions over the years have speculated about whether large-brand redirectors could be abused. We found no authoritative evidence that go.microsoft.com functions as a free-form open redirector to arbitrary, non-Microsoft destinations. In our spot checks and long familiarity with the ecosystem, the links resolve to official Microsoft endpoints, though old content may yield retired pages. The critical point remains: when a link arrives unexpectedly, verify the sender and context before clicking, then verify the final domain and branding after the redirect completes.
User feedback
Public commentary about go.microsoft.com tends to focus on convenience, localization, and the occasional frustration when an older link no longer leads to the exact article one expects. We did not find substantive, verifiable complaints alleging that this specific subdomain was the origin of fraud. The most common usability gripe is encountering a generic landing page or a 404 due to documentation reorganization, a normal occurrence in large knowledge bases that are continually maintained. Such experiences do not, in themselves, suggest deceptive intent.
Where confusion can arise is in the broader fraud environment, where attackers frequently imitate Microsoft’s brand. Phishing emails often display Microsoft logos and design motifs, sometimes incorporating deceptive domains with subtle typos or hyphenated lookalikes. A go.microsoft.com link inside an email from an unknown sender is not proof of legitimacy—attackers could place a real Microsoft link beside a malicious attachment or pair it with a second, harmful link elsewhere in the message. The safest habit is to verify the message source and independently navigate to Microsoft’s official site if something seems urgent or unusual.
A small subset of users report encountering redirect loops or unexpected language selection results. These issues typically trace to browser privacy settings, cookie behavior, or geo-targeting assumptions that don’t align with the user’s preferences. Clearing cookies or explicitly choosing a regional site often resolves the experience. Again, that is more indicative of routine web localization dynamics rather than any misconduct specific to the go.microsoft.com redirector.
Deposits & withdrawals
There are no deposit, withdrawal, or payment functions on go.microsoft.com itself. The domain exists to route traffic to official resources, not to collect funds or handle transactions. If your click ultimately takes you to a Microsoft Store page or a subscription management section, those flows occur under the store or account subdomains with their own payment processors and clear branding. Any demand for cryptocurrency, gift cards, or wire transfers connected to a link claiming to be Microsoft support should be treated as a red flag for a scam.
Legitimate Microsoft sign-in prompts typically occur on domains such as login.live.com or microsoftonline.com, each protected by a valid certificate and familiar interface elements. If you are asked to sign in after following a go.microsoft.com link, confirm the domain before entering credentials. Look carefully for typos (for example, extra hyphens or swapped characters) and ensure the URL retains the Microsoft identity. If something feels off—especially if the page is pushing urgent payment—stop and navigate manually from microsoft.com or support.microsoft.com to locate the same resource.
For downloads, Microsoft distributes official installers and updates from its own infrastructure. Before running any downloaded file reached via a redirect, confirm file details and consider checking the publisher signature in the file’s properties. Modern Windows protections like SmartScreen will also provide warnings for unrecognized executables. If a download does not present a verified Microsoft signature or triggers unusual prompts, do not proceed.
Why unregulated brokers are risky
While regulatory licensing is not relevant to a redirector, general trust hygiene still applies whenever a link takes you from one page to another. Redirects obscure the final destination at a glance, so treat every click as a two-step verification process: check the link’s apparent source, then confirm the destination’s domain and branding after the hop. This habit prevents a surprising amount of social engineering success, where urgency and authority cues steer users past their normal skepticism.
Attackers capitalize on well-known brands, and Microsoft is among the most impersonated globally. Scammers may place a genuine Microsoft redirect link in a message to feign legitimacy while the actual harm happens through a different link, an attachment, or a phone callback number in the same communication. Others register deceptive lookalike domains that visually resemble Microsoft’s naming conventions. Staying grounded in domain verification—reading the address bar carefully and not relying solely on logos—helps counter these tactics.
The best mitigation is to rely on independently initiated navigation for high-stakes actions. If an email prompts you to review billing, reset a password, or install critical updates, don’t click through; open a new browser tab and go directly to microsoft.com or your known account portal. This simple step breaks many common attack chains. It also ensures that, even when a legitimate redirector is used properly, you remain in control of the journey.
How to get help if you’ve been scammed
If you suspect you paid a fraudster after following a link you believed was from Microsoft, contact your bank or card issuer immediately and request a chargeback or dispute. Explain that you may have been the victim of a social engineering or impersonation scam and ask the institution to freeze or reissue your card if appropriate. Time is critical—rapid reporting increases the chance of stopping or reversing transactions. Document the timeline, the message you received, and the exact link you clicked to support your claim.
Next, file a report with the relevant authorities. In the United States, report to the Federal Trade Commission and submit details to IC3.gov; in the United Kingdom, use Action Fraud; in the EU and other regions, consider econsumer.gov or your national cybercrime reporting channel. Preserve emails, screenshots, transaction receipts, and chat logs—these materials assist investigations and can help institutions detect broader patterns. If your Microsoft account credentials might have been exposed, change your password and enable two-step verification immediately.
For tailored guidance and escalation support, contact our team at reportscammedfunds.pro. We can review your documentation, help map the payment rails involved, and coordinate with your bank on chargeback procedures where applicable. While no recovery can be guaranteed, a structured, evidence-led approach materially improves outcomes. Reach out to reportscammedfunds.pro as soon as possible so we can assess your case and advise on the best next steps.
Conclusion
On balance, go.microsoft.com is a legitimate, brand-controlled redirector subdomain used widely across Microsoft’s ecosystem. Our assessment aligns with its role as a navigation aid rather than a transactional platform. The primary risk is not the domain itself, but the broader practice of blindly trusting links—especially in unsolicited messages that trade on the Microsoft name.
Exercise ordinary diligence with any redirect: verify the context before you click and the destination afterward. If you reach a login or payment page, scrutinize the domain and certificate details, and consider navigating directly from microsoft.com instead of relying on the link. Broken or outdated links are an annoyance, but they are not, in themselves, evidence of malfeasance.
For everyday users and enterprise teams alike, the conclusion is straightforward. Treat go.microsoft.com as safe when encountered in official materials, but remain vigilant about the possibility of spoofed communications that try to borrow Microsoft’s credibility. When in doubt, pause, verify through independent navigation, and seek help promptly if something goes wrong.