Trading platform & site functionality
Gmail is a widely used webmail service accessible through browsers, mobile apps, and standard email protocols such as IMAP and POP. The core experience lives at gmail.com and mail.google.com, with authentication managed through accounts.google.com. It integrates tightly with the Google Account ecosystem, giving users access to Google Drive for large attachments, Calendar for scheduling, and Meet for video calls. The interface is mature and features powerful search, labels, filters, and context-aware suggestions that make inbox management efficient even at high volumes.
Security controls are prominent. Gmail enforces HTTPS across its web interface, and messages are typically transmitted with TLS between participating mail servers. Users can enable two-factor authentication (2FA), including app-based codes and hardware security keys, significantly reducing the risk of account takeover. The platform layers machine learning–driven spam and phishing detection, banners warning about suspicious senders, and additional identity signals for verified domains to help users judge whether a message is genuine. While no filter is perfect, the combination of technical standards like SPF/DKIM/DMARC and Gmail’s heuristics provides a robust baseline of protection.
Practical reliability is a hallmark. Gmail benefits from Google’s globally distributed infrastructure and redundant data centers, resulting in strong uptime and swift performance in most regions. Storage allocations are generous in the free tier and expandable through paid offerings, and the service interoperates well with desktop clients using OAuth for permissioned access. Users should still be careful during sign-in: always confirm the domain in the browser address bar is gmail.com or accounts.google.com, and be skeptical of lookalike login pages that try to harvest credentials. Those simple checks, coupled with 2FA, close off the most common attack paths.
License & regulatory status
Gmail is a communications service, not a broker, exchange, or investment product. As such, it does not fall under financial conduct regulators like the FCA in the United Kingdom, BaFin in Germany, ASIC in Australia, or the CFTC in the United States. You should not expect financial compensation schemes, investor protection coverage, or leverage caps to apply to an email account. The proper frame of due diligence is security, privacy, and account integrity rather than financial regulation.
From a privacy standpoint, Google’s operations are subject to data-protection frameworks and local laws, such as Europe’s GDPR and California’s privacy rules. Google’s public-facing materials discuss data handling and provide account-level controls like security checkups and activity dashboards, though those documents are not the same as a regulatory license. Transparency reports and whitepapers exist, but we do not treat them as a substitute for independent verification by a financial regulator because that simply is not the relevant lens here. Users evaluating Gmail should instead weigh how the company discloses data practices and provides user control mechanisms.
A recurring confusion in scam narratives is the misuse of regulator names to confer false legitimacy on communications. We have seen boiler-room pitches and advance-fee fraud emails that claim their Gmail-based outreach is “approved by” the FCA or “certified by” ESMA or BaFin — this is marketing theater, not reality. Regulators do not endorse email senders or certify email accounts; at best, they may publish warnings about specific fraudulent schemes. If a message claims regulatory blessing yet comes from a generic Gmail address, treat it as a bright-red indicator to verify independently via the regulator’s official warning list.
User feedback
User feedback around Gmail generally splits into two streams: security/usability and abuse originating elsewhere. On the security front, many users praise the reliability and spam filtering, yet some report friction when accounts are locked for suspicious activity or when recovery loops are difficult to complete. Complaints often center on the lack of direct human support for free accounts, especially when phone numbers or recovery emails are outdated. These lockouts frustratedly appear to users as “sudden” despite being triggered by real risk signals such as password leaks or suspicious login attempts.
On abuse, it’s important to separate the platform from bad actors. Criminals frequently use Gmail addresses for outreach because the domain is familiar, and that familiarity can lower a target’s guard. We routinely encounter lottery scams, fake shipping notices, and impersonations of banks, delivery firms, or tech support, all sent from Gmail or spoofing Gmail-like addresses. The same is true for romance fraud (“pig butchering”) and boiler-room investment pitches that pressure victims to move to off-platform chats, ultimately steering them into crypto transfers or advance fees.
Filtering is strong but not flawless. Some legitimate mail lands in spam, and some phish slip through to the inbox, particularly when attackers mirror a victim’s recent real correspondence or compromise a contact’s account. Workspace (paid) customers report better support experiences and admin-level tools to contain compromises, while consumers rely more on automated systems and help articles. None of this discredits gmail.com as a domain; it underlines the need to maintain recovery options, enable 2FA, and treat urgent financial requests in email as inherently suspect until verified.
Deposits & withdrawals
Gmail does not involve deposits or withdrawals in the financial sense, so the practical analogue is account access and data control. New accounts are free, and you can secure them with two-factor authentication, backup codes, and a recovery email or phone number. If you’ve granted third-party apps access, manage those permissions in the Google Account’s security dashboard to prevent rogue clients from persisting after a password change. This is the email equivalent of controlling the “funds”—your messages, contacts, and identity credentials—so ensure you can always reassert control.
If you need to extract your data, Google Takeout allows export of mail (via MBOX) and contacts, enabling migration to another provider or an offline backup. Consider scheduling periodic exports for high-stakes accounts used in business or legal contexts, just as you would keep bank statements or contracts archived. If a compromise occurs, change the password, revoke all third-party access, log out active sessions, and rotate recovery methods before initiating a fresh Takeout to avoid exporting tampered content. Document the steps and timestamps to assist any later investigation.
Should you decide to close an account, the deletion workflow is available in the Google Account settings, with warnings about permanence and linked services. Before closing, transfer ownership of shared documents, update critical service logins that rely on the Gmail address, and download a final archive. Be cautious of impostors: no genuine Google support agent will ask for your one-time codes or payment to “unlock” or “recover” a free Gmail account — that is a classic recovery scam. Always initiate sensitive account actions from within accounts.google.com and verify the URL carefully.
Why unregulated brokers are risky
Although Gmail is not a financial platform, the stakes tied to your mailbox can be financial. Attackers who gain access to your email often pivot to reset passwords on banking, brokerage, and crypto accounts. That makes 2FA and strong, unique passwords non-negotiable, preferably secured with a hardware key wherever supported. Treat every login prompt with suspicion, especially if you arrived via a link in an email; it takes only one convincing phishing page to compromise an entire digital life.
Another risk vector is social engineering. Criminals may send invoices, change-of-bank notices, or executive impersonations to induce wire transfers or crypto payments, a pattern often called business email compromise. Even with DMARC and other controls, a determined attacker can spoof display names or reply-to fields to blend into a thread. Build procedures that require out-of-band verification for payment changes, and keep finance staff trained to spot urgency tactics, mismatched domains, and subtle formatting tells.
Because Gmail is a ubiquitous brand, its look and feel are often copied. Fake “Gmail storage full” notices and “account suspension” alerts are common lures, sometimes linking to credible-seeming pages that are not on google.com. Bookmark genuine login pages and avoid searching for login links, as ads can be abused to redirect to phishing. When in doubt, manually type gmail.com or accounts.google.com, and confirm the browser indicates a secure, valid connection before entering credentials.
How to get help if you’ve been scammed
If you have already sent money following an email request — whether through card, bank wire, or crypto — act fast. Contact your bank or card issuer immediately to attempt a chargeback or recall and flag the transaction as fraud; in the U.S., also report via IC3.gov, and in the U.K., use Action Fraud, then notify local police as advised. Preserve all evidence: full message headers, attachments, transaction IDs, and chat logs. Then reach out to reportscammedfunds.pro for case assistance; our team can help you structure bank disputes, prepare regulator reports, and trace on-chain assets where possible.
If the problem is account compromise or a suspicious message rather than a completed payment, use Gmail’s “Report phishing” and “Report spam” tools to submit samples, and begin recovery via accounts.google.com/signin/recovery. Change your password, revoke third-party access, check forwarding rules and filters for tampering, and enable 2FA. Do not pay any service that promises “guaranteed recovery” or asks for an upfront fee to unlock your mailbox — that is the essence of a recovery scam. For businesses, notify your IT and legal teams so they can evaluate exposure and regulatory obligations.
For complex, cross-border cases, consult the appropriate national authority: for example, the FTC in the United States, your data protection authority in the EU, or your local cybercrime unit. Keep a timeline of events, copies of emails with headers, and any screenshots of fraudulent websites you interacted with. If funds have moved, time is critical; after alerting your bank, contact reportscammedfunds.pro to coordinate next steps and to understand viable recovery avenues. We cannot promise reversals, but early, well-documented action materially improves outcomes.
Conclusion
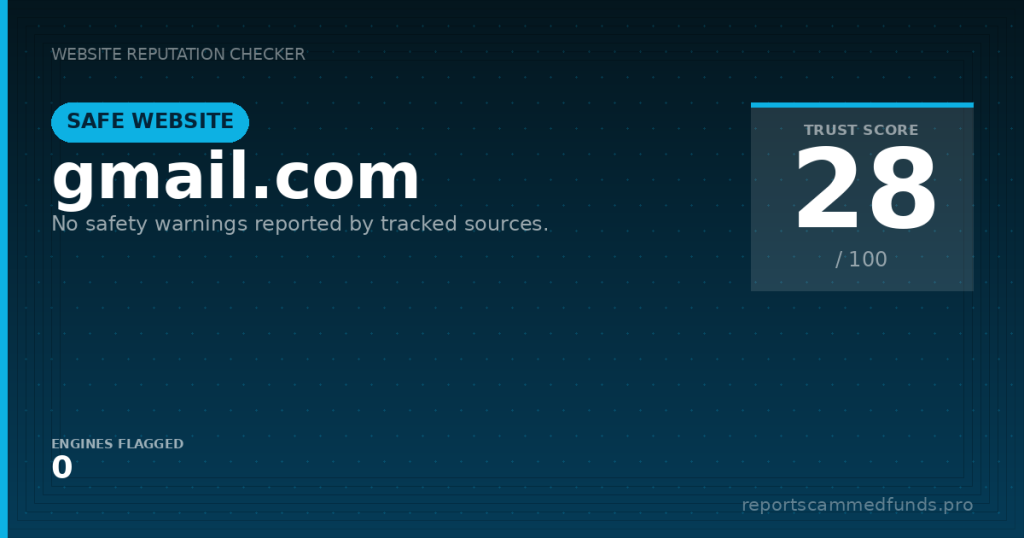
On the evidence, gmail.com is a safe and legitimate domain operated by Google LLC, with mature infrastructure and industry-standard security controls. The dominant risks are not about the domain itself but about how criminals exploit trust in the brand, send convincing impostor emails, or clone login pages. Users who practice cautious sign-in habits and employ robust account security can minimize exposure substantially.
Our recommendation is straightforward: continue using Gmail if it suits your needs, but layer in best practices. Verify you are on gmail.com or accounts.google.com before entering credentials, enable two-factor authentication with a hardware key if possible, and scrutinize payment requests received by email. For high-value use cases, add procedures like callback verification for banking changes and restrict third-party app access to the minimum necessary.
We rate gmail.com as a Safe Website while urging readers to remain skeptical of unsolicited messages and to be wary of recovery scams offering quick fixes. Trust the domain, not the story in the email; confirm through independent channels when money or sensitive data are at stake. Should anything go wrong, act swiftly with your bank, your local authority, and engage reportscammedfunds.pro for structured help.